
Welcome to Veilio !
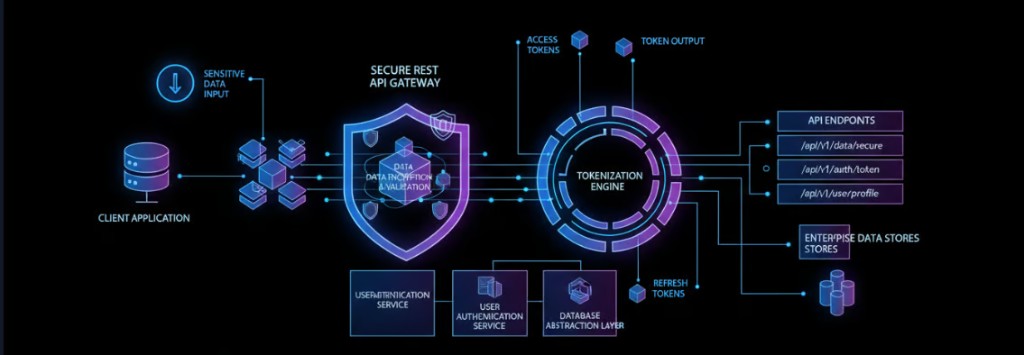
Veilio helps you protect sensitive customer data by replacing raw values (email, phone, IDs) with secure tokens.
Your application stores tokens. When needed, your backend can retrieve original values with controlled detokenization calls.
Why teams integrate Veilio
- Reduce sensitive data exposure in application databases
- Keep existing product workflows with minimal code changes
- Improve auditability and compliance readiness (GDPR, crypto-shredding, SIEM)
What you will build in this guide
- Generate and configure an API key
- Tokenize a sensitive value
- Store and use the returned token
- Detokenize only when needed
- Ship to production with security best practices
Integration paths
| Path | Best for |
|---|---|
| Quickstart | First working flow in 5 minutes (curl) |
| SDK Javascript | Node.js / TypeScript backends |
| SDK Python | Python backends |
| HTTP Integration | Any language, full control |
| API Reference | Complete endpoint list |
Jump right in
Advanced topics
| Topic | Page |
|---|---|
| Historical CRM import | Migration Mode |
| Account exit / portability | Offboarding |
| Dataset upload & sharing | Datasets Upload |
| Retention & shredding | Data Lifecycle |
| Latency & throughput | Performance |
| Go-live checklist | Go-live Checklist |
Related links
- Product website: https://veilio.fr
- Documentation: https://veilio.fr/docs
- Contact / Demo: https://veilio.fr/contact